Trust has always been central to affiliate marketing, but in an industry where significant volumes of data and revenue pass through third-party technology, trust alone is no longer enough.
Operators rely on affiliate platforms to track performance, manage commissions and safeguard commercially sensitive information. Affiliates, meanwhile, depend on those same systems to ensure their earnings are calculated accurately and reported transparently.
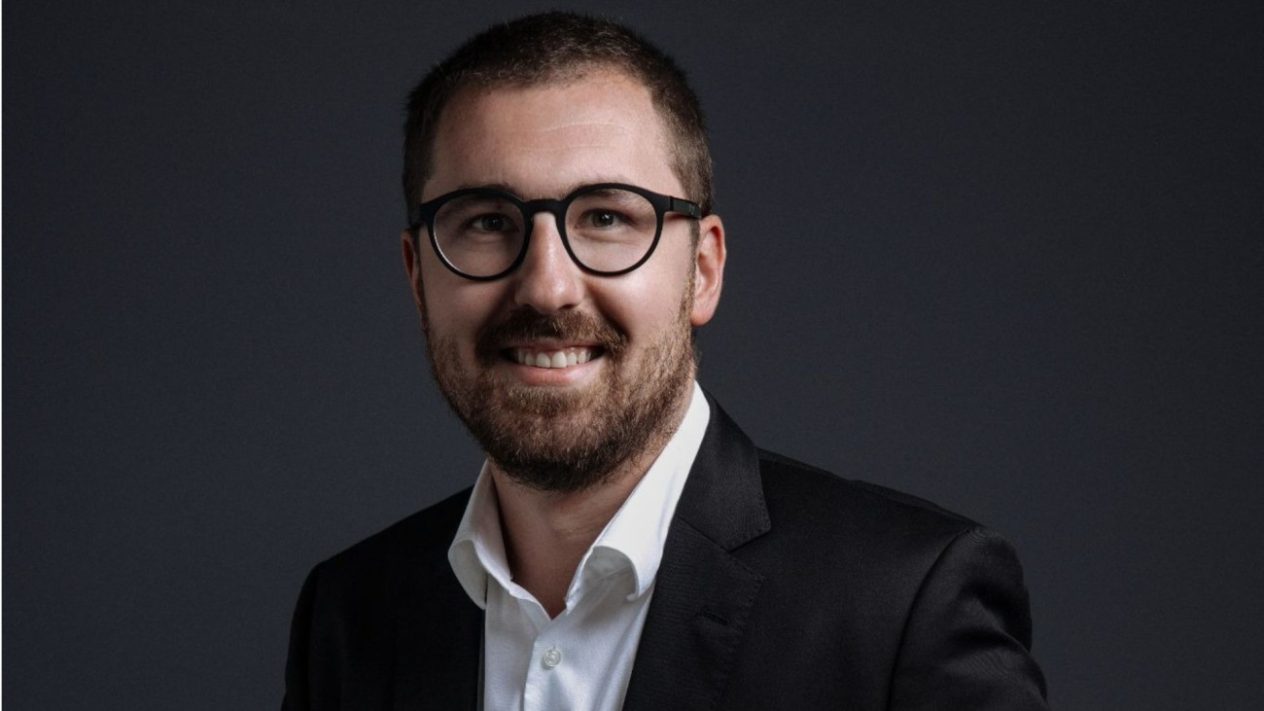
For Vlad Bondarenko, Chief Product Officer at ReferOn, this creates a responsibility that extends beyond simply delivering functional technology.
He said: “Affiliate software sits in an uncomfortable position. Operators push their reporting through us, affiliates treat our numbers as the basis for their income, and neither side gets to open the box and check what’s actually happening inside it.
“What’s left is trust, which is a thin thing to run a business on.”
The challenge, Bondarenko believes, is that security has historically been treated as something to address once a platform’s architecture is already established.
While this approach may satisfy immediate operational requirements, it can create vulnerabilities that become increasingly difficult to resolve as the business grows.
“On most platforms, security turns up late,” explained Bondarenko. “Not out of negligence, and I’ve yet to see anybody argue against it in a planning meeting, it’s simply never the thing that’s currently on fire.”
ReferOn has taken a different approach, using the rebuilding of its infrastructure as an opportunity to make security a fundamental part of the platform rather than an additional layer of protection.
Closing the gaps before they appear
One of the most significant challenges facing established technology platforms is the gradual accumulation of complexity.
As new integrations, services and client requirements emerge, infrastructure can develop additional access points that are difficult to monitor consistently.
ReferOn addresses this through a centralised entry point, using Cloudflare as the reverse proxy for all incoming platform traffic.
Its infrastructure operates on Amazon Web Services (AWS), with Kubernetes managing services across geographically distributed nodes. Web application firewall protection, rate limiting and distributed denial-of-service (DDoS) mitigation are applied through Cloudflare.
For Bondarenko, the value lies less in the individual security tools and more in ensuring that every request follows the same controlled route.
He stated: “Plenty of platforms have all three of those. What matters more is that there is only one door. One place to watch traffic, one place to apply a rule, one place where a change is visible to anyone who looks.”
This principle extends to how infrastructure changes are managed.
Rather than relying on manual adjustments, ReferOn defines its infrastructure through code, allowing changes to be documented, reviewed and reproduced consistently.
According to Bondarenko, this removes the risk of undocumented fixes gradually creating differences between how a platform is supposed to operate and how it actually functions.
Why performance is also a security issue
Security discussions typically focus on preventing unauthorised access, but Bondarenko argues that resilience under pressure deserves equal attention.
A platform struggling to handle traffic spikes can introduce operational risks, particularly when accurate attribution and commission calculations depend on uninterrupted processing.
“Capacity usually gets filed under performance rather than security, and I think that’s a mistake,” Bondarenko said. “A system with no headroom left fails in ways nobody planned for.”
ReferOn reports that its redirect service handles more than 4,000 requests per second across six instances while maintaining CPU utilisation below 50%.
The platform also records a 95th-percentile redirect latency of 4.8 milliseconds and a 99th-percentile latency of five milliseconds, measured at service level.
These figures, Bondarenko explains, demonstrate the importance of maintaining sufficient capacity rather than operating close to infrastructure limits.
“We’re not near the edge of anything, so a traffic spike from a big campaign launch is a Tuesday rather than an incident,” he stated.
Keeping operator data separate
Past maintaining availability, affiliate technology providers must also ensure that information belonging to one operator cannot become accessible to another.
ReferOn uses a tenant-based architecture in which every record is assigned to a specific client environment. This creates logical boundaries around each operator’s affiliates, tracking links and reporting information.
“Either a request resolves inside the tenant boundary, or it doesn’t resolve at all,” Bondarenko explained.
For operators requiring additional isolation, ReferOn also offers dedicated databases or Kubernetes clusters, allowing infrastructure arrangements to be determined during onboarding.
The separation extends to administrative interfaces, affiliate portals and testing environments, with production access restricted by IP address.
Another important consideration is the amount of personal information required to perform attribution.
ReferOn’s tracking system uses internally generated tracking and click identifiers, allowing commission calculations and reporting to operate without needing to identify the individual player.
Bondarenko explained: “Commission logic, reward calculation and reporting all work off those two. Nowhere in that chain does anything need to resolve who the player behind the click actually is.”
Removing unnecessary access and human error
Bondarenko identifies developer access to production environments as one area where unnecessary risks can emerge.
ReferOn’s engineers work locally without access to production clusters, reducing the possibility of sensitive credentials being exposed through development activity.
Bondarenko stated: “Our engineers work locally. A developer needs no network access at all to be fully productive, and has no access to production clusters whatsoever.”
Changes are instead introduced through automated pipelines, with functionality tested in isolated environments before being released gradually. Feature flags also allow individual capabilities to be disabled quickly if problems arise.
Access permissions are managed centrally, while internal users are required to use two-factor authentication.
In an industry where disputes over affiliate earnings can damage commercial relationships, Bondarenko sees this as particularly valuable.
He said: “In a market where affiliates more or less assume the numbers get quietly adjusted after the fact, being able to show them a record that physically cannot be altered is worth a good deal more than telling them it wasn’t.”
Building resilience into the platform
Security also depends on what happens when infrastructure fails.
ReferOn operates at least three instances of each application across separate AWS availability zones, reducing reliance on any single physical location.
Transactional data is maintained through Amazon RDS with automatic failover and point-in-time recovery, while analytical information is backed up daily to Amazon S3.
Supporting components, including message queues and caches, are designed to prevent individual failures from disrupting core operations.
Bondarenko believes this separation is particularly important because unexpected failures can expose weaknesses that remain hidden during normal operations.
He commented: “That’s an uptime argument, obviously, but it’s a security argument as well, because a chain of failures is exactly the situation in which systems start improvising.”
Turning security into accountability
Ultimately, Bondarenko believes operators should expect more from their technology partners than general assurances about security. They should be able to understand where their information is stored, who can access it and what safeguards exist when something goes wrong.
ReferOn provides detailed security questionnaires, data-flow documentation and access-control information under non-disclosure agreements during technical due diligence.
For Bondarenko, transparency should be an ongoing responsibility rather than a last-minute requirement during commercial negotiations.
He concluded:”If you can’t get a straight answer about where your data sits, who can reach it and what happens when something breaks, that’s worth doing something about, whoever your provider is.”
Bondarenko’s message is straightforward: security should be built into the foundations of affiliate technology, not added once those foundations have already been established.
“Your data stays yours. You should be able to see exactly how.”